Saturday, May 30, 2020

Thursday, May 28, 2020
You are invited to a Small Business Discussion with Senator Bennet - NEW LINK to RSVP
|



Saturday, May 23, 2020
Senator Bennet’s Weekly Update
|


You are Invited to a Call to Learn About Health Force with Senator Bennet
|

Friday, May 22, 2020
Ethical Hacking Platform For Penetration Testing | How To Hack The Invite Code: Join Hack The Box (HTB)

Hack The Box
Hack The Box (HTB) is a free platform available to ethical hackers to do a penetration testing for ethical hacking projects. It consist of different type of challenges that are updated constantly. Some of the challenges related to the real world scenarios and rest of the challenges related to learning towards a CTF style of challenges.Before joining to HTB, there is a simple task for you to prove your skills after that you'll able to create an account, and then you'll be able to access to your HTB Lab, where several challenges await for you to hack them. That's the beginning step for all of us to joining this. If you got success while hacking then you'll get points.
Task For Joining The HTB
Before joining the HTB, there is a task to hack invite code and paste that code in the code box for further registration to your account. You can complete a simple challenge to prove your skills, if you don't hack that then here is a short video below this content about hacking the invite code. Watch the video and hack the code!
In this Video you'll learn about How to join Hack the box (HTB) in Kali Linux and other Linux Distributions.
More info
Thursday, May 21, 2020

How To Start | How To Become An Ethical Hacker
Are you tired of reading endless news stories about ethical hacking and not really knowing what that means? Let's change that!
This Post is for the people that:
- Have No Experience With Cybersecurity (Ethical Hacking)
- Have Limited Experience.
- Those That Just Can't Get A Break

OK, let's dive into the post and suggest some ways that you can get ahead in Cybersecurity.
I receive many messages on how to become a hacker. "I'm a beginner in hacking, how should I start?" or "I want to be able to hack my friend's Facebook account" are some of the more frequent queries. Hacking is a skill. And you must remember that if you want to learn hacking solely for the fun of hacking into your friend's Facebook account or email, things will not work out for you. You should decide to learn hacking because of your fascination for technology and your desire to be an expert in computer systems. Its time to change the color of your hat 😀
I've had my good share of Hats. Black, white or sometimes a blackish shade of grey. The darker it gets, the more fun you have.
If you have no experience don't worry. We ALL had to start somewhere, and we ALL needed help to get where we are today. No one is an island and no one is born with all the necessary skills. Period.OK, so you have zero experience and limited skills…my advice in this instance is that you teach yourself some absolute fundamentals.
Let's get this party started.
- What is hacking?
Hacking is identifying weakness and vulnerabilities of some system and gaining access with it.
Hacker gets unauthorized access by targeting system while ethical hacker have an official permission in a lawful and legitimate manner to assess the security posture of a target system(s)There's some types of hackers, a bit of "terminology".
White hat — ethical hacker.
Black hat — classical hacker, get unauthorized access.
Grey hat — person who gets unauthorized access but reveals the weaknesses to the company.
Script kiddie — person with no technical skills just used pre-made tools.
Hacktivist — person who hacks for some idea and leaves some messages. For example strike against copyright.
- Skills required to become ethical hacker.
- Curosity anf exploration
- Operating System
- Fundamentals of Networking
CEH: Fundamentals Of Social Engineering

Social engineering is a nontechnical method of breaking into a system or network. It's the process of deceiving users of a system and convincing them to perform acts useful to the hacker, such as giving out information that can be used to defeat or bypass security mechanisms. Social engineering is important to understand because hackers can use it to attack the human element of a system and circumvent technical security measures. This method can be used to gather information before or during an attack.
A social engineer commonly uses the telephone or Internet to trick people into revealing sensitive information or to get them to do something that is against the security policies of the organization. By this method, social engineers exploit the natural tendency of a person to trust their word, rather than exploiting computer security holes. It's generally agreed that users are the weak link in security; this principle is what makes social engineering possible.
The most dangerous part of social engineering is that companies with authentication processes, firewalls, virtual private networks, and network monitoring software are still wide open to attacks, because social engineering doesn't assault the security measures directly. Instead, a social-engineering attack bypasses the security measures and goes after the human element in an organization.
Types of Social Engineering-Attacks
There are two types of Social Engineering attacksHuman-Based
Human-based social engineering refers to person-to-person interaction to retrieve the desired information. An example is calling the help desk and trying to find out a password.Computer-Based
Computer-based social engineering refers to having computer software that attempts to retrieve the desired information. An example is sending a user an email and asking them to reenter a password in a web page to confirm it. This social-engineering attack is also known as phishing.Human-Based Social Engineering
Human-Based further categorized as follow:Impersonating an Employee or Valid User
In this type of social-engineering attack, the hacker pretends to be an employee or valid user on the system. A hacker can gain physical access by pretending to be a janitor, employee, or contractor. Once inside the facility, the hacker gathers information from trashcans, desktops, or computer systems.Posing as an Important User
In this type of attack, the hacker pretends to be an important user such as an executive or high-level manager who needs immediate assistance to gain access to a computer system or files. The hacker uses intimidation so that a lower-level employee such as a help desk worker will assist them in gaining access to the system. Most low-level employees won't question someone who appears to be in a position of authority.Using a Third Person
Using the third-person approach, a hacker pretends to have permission from an authorized source to use a system. This attack is especially effective if the supposed authorized source is on vacation or can't be contacted for verification.Calling Technical Support
Calling tech support for assistance is a classic social-engineering technique. Help desk and technical support personnel are trained to help users, which makes them good prey for social-engineering attacks.Shoulder Surfing
Shoulder surfing is a technique of gathering passwords by watching over a person's shoulder while they log in to the system. A hacker can watch a valid user log in and then use that password to gain access to the system.Dumpster Diving
Dumpster diving involves looking in the trash for information written on pieces of paper or computer printouts. The hacker can often find passwords, filenames, or other pieces of confidential information.Computer-Based Social Engineering
Computer-based social-engineering attacks can include the following:- Email attachments
- Fake websites
- Pop-up windows
Insider Attacks
If a hacker can't find any other way to hack an organization, the next best option is to infiltrate the organization by getting hired as an employee or finding a disgruntled employee to assist in the attack. Insider attacks can be powerful because employees have physical access and are able to move freely about the organization. An example might be someone posing as a delivery person by wearing a uniform and gaining access to a delivery room or loading dock. Another possibility is someone posing as a member of the cleaning crew who has access to the inside of the building and is usually able to move about the offices. As a last resort, a hacker might bribe or otherwise coerce an employee to participate in the attack by providing information such as passwords.Identity Theft
A hacker can pose as an employee or steal the employee's identity to perpetrate an attack. Information gathered in dumpster diving or shoulder surfing in combination with creating fake ID badges can gain the hacker entry into an organization. Creating a persona that can enter the building unchallenged is the goal of identity theft.Phishing Attacks
Phishing involves sending an email, usually posing as a bank, credit card company, or other financial organization. The email requests that the recipient confirm banking information or reset passwords or PINs. The user clicks the link in the email and is redirected to a fake website. The hacker is then able to capture this information and use it for financial gain or to perpetrate other attacks. Emails that claim the senders have a great amount of money but need your help getting it out of the country are examples of phishing attacks. These attacks prey on the common person and are aimed at getting them to provide bank account access codes or other confidential information to the hacker.Online Scams
Some websites that make free offers or other special deals can lure a victim to enter a username and password that may be the same as those they use to access their work system.The hacker can use this valid username and password once the user enters the information in the website form. Mail attachments can be used to send malicious code to a victim's system, which could automatically execute something like a software keylogger to capture passwords. Viruses, Trojans, and worms can be included in cleverly crafted emails to entice a victim to open the attachment. Mail attachments are considered a computer-based social-engineering attack.
More info
Hacking All The Cars - Part 2
Connecting Hardware to Your Real Car:
I realized the other day I posted Part 2 of this series to my youtube awhile ago but not blogger so this one will be quick and mostly via video walkthrough. I often post random followup videos which may never arrive on this blog. So if you're waiting on something specific I mentioned or the next part to a series its always a good idea to subscribe to the YouTube. This is almost always true if there is video associated with the post.
In the last blog we went over using virtual CAN devices to interact with a virtual car simulators of a CAN network This was awesome because it allowed us to learn how to interact with he underlying CAN network without fear of hacking around on an expensive automobile. But now it's time to put on your big boy pants and create a real CAN interface with hardware and plug your hardware device into your ODB2 port.
The video I created below will show you where to plug your device in, how to configure it and how to take the information you learned while hacking around on the virtual car from part1 and apply it directly to a real car.
Video Walk Through Using Hardware on a Real Car
As a reference here are the two device options I used in the video and the needed cable:
Hardware Used:
Get OBD2 Cable:
https://amzn.to/2QSmtyL
Get CANtact:
https://amzn.to/2xCqhMt
Get USB2CAN:
https://shop.8devices.com/usb2can
https://amzn.to/2QSmtyL
Get CANtact:
https://amzn.to/2xCqhMt
Get USB2CAN:
https://shop.8devices.com/usb2can
Creating Network Interfaces:
As a reference here are the commands from the video for creating a CAN network interface:
USB2Can Setup:
The following command will bring up your can interface and you should see the device light color change:
sudo ip link set can0 up type can bitrate 125000
Contact Setup:
Set your jumpers on 3,5 and 7 as seen in the picture in the video
Sudo slcand -o -s6 /dev/ttyACM can0 <— whatever device you see in your DMESG output
Ifconfig can0 up
Summary:
That should get you started connecting to physical cars and hacking around. I was also doing a bit of python coding over these interfaces to perform actions and sniff traffic. I might post that if anyone is interested. Mostly I have been hacking around on blockchain stuff and creating full course content recently so keep a look out for that in the future.
Read more
- Curso De Hacking Etico Gratis
- Hardware Hacking
- Hacking Health
- Hacker Etico
- Significado Hacker
- Herramientas De Seguridad Informatica
- Javascript Hacking
- Growth Hacking Tools
- Hacking Net
- Que Significa Hat
- Hacking Apps
- Hacking Forums
- Hacking Wifi Windows
- Libros Para Aprender A Hackear
- Hacking Smart Tv
- Hacking Cracking
Wednesday, May 20, 2020
5 Free Online Courses To Learn Artificial Intelligence
We are living in the era of fourth industrial revolution(4IR), where Artificial intelligence has a significant role to play. This 4IR technology embedded within societies and even into the human body. From Computer enthusiasts to common people, everyone should be aware and learn this breakthrough technology.
We think about gigantic Robots from Transformers when we hear about Artificial Intelligence(AI) which is a fiction in the past but a fact today, capable of transforming the whole tech world. The field of AI consists of more than Robots such as personal assistants, self-driving cars, apprenticeship learning, behavior cloning and so on. To learn about this advanced technology, thanks to the online learning resources which offers great content to get started with artificial intelligence.
Here are the 5 free e-learning courses on Artificial Intelligence
1. UC Berkeley CS188 Intro to AI
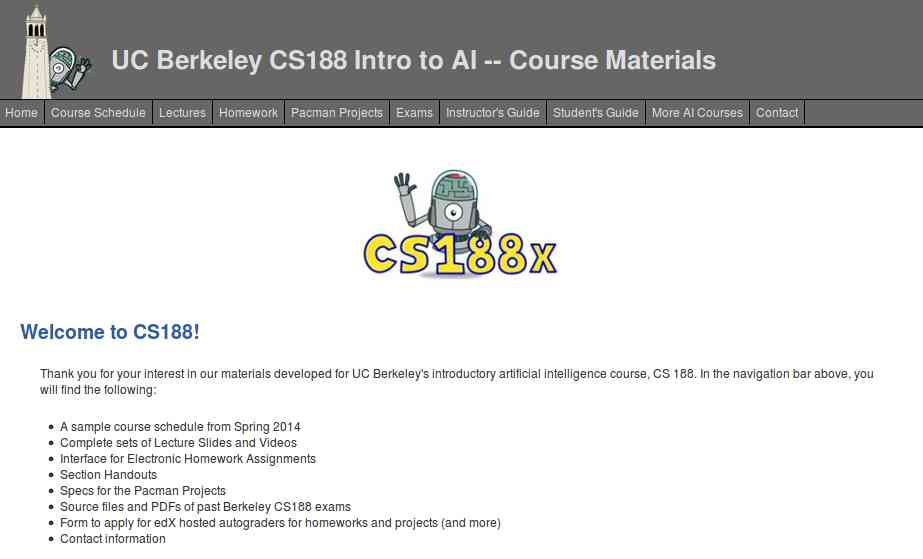
Get started with UC Berkeley AI course, this course is absolutely for beginners who are unaware of Artificial intelligence. It doesn't need any prior computer knowledge to know about AI. UC Berkeley allows anyone to learn this course for free. This course is systematically presented and consists of the following:
- Course Schedule
- Complete sets of Lecture Slides and Videos
- Interface for Electronic Homework Assignments
- Section Handouts
- Specs for the Pacman Projects
- Source files and PDFs of past Berkeley CS188 exams
- Form to apply for edX hosted autograders for homework and projects (and more)
- Contact information
Aside from this, you can also browse the following courses as well from UC Berkeley that are part of AI course:
- Machine Learning: CS189, Stat154
- Intro to Data Science: CS194-16
- Probability: EE126, Stat134
- Optimization: EE127
- Cognitive Modeling: CogSci131
- Machine Learning Theory: CS281A, CS281B
- Vision: CS280
- Robotics: CS287
- Natural Language Processing: CS288
2. Artificial Intelligence: Principles and Techniques
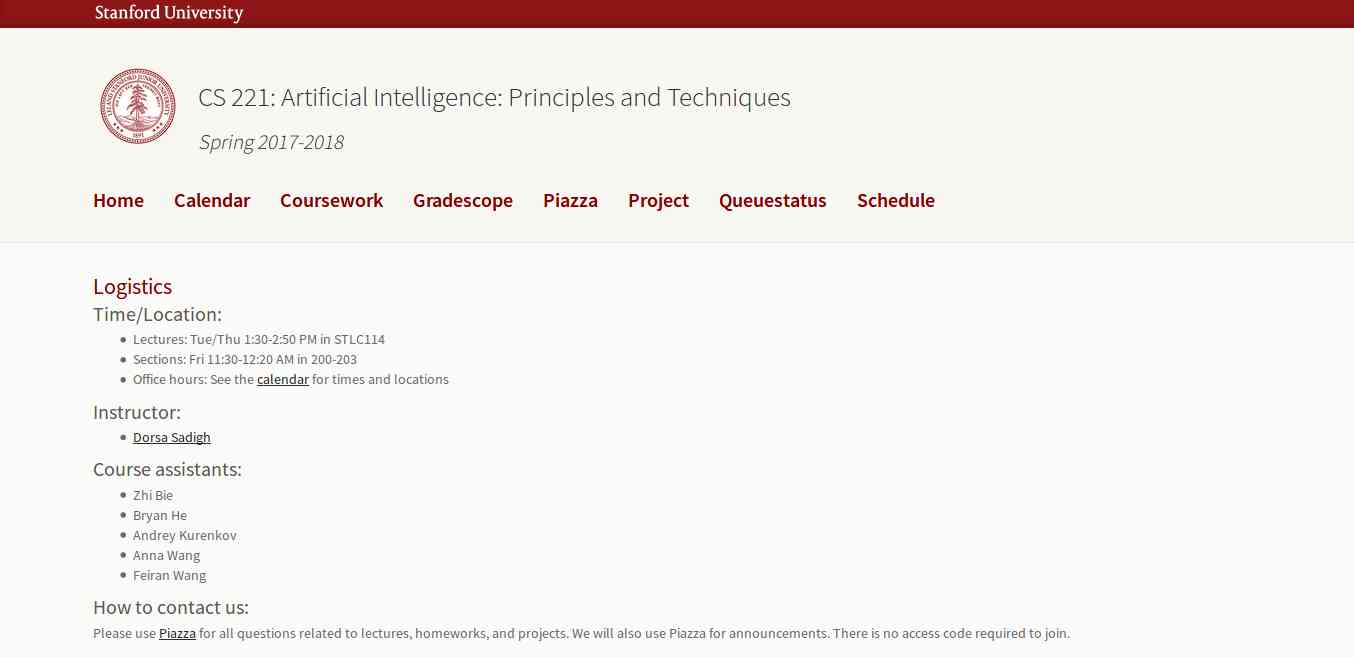
This course is offered by Stanford with great content that includes topics, videos, assignments, projects, and exams. The whole course mainly focuses on the complex real-world problems and try to find similarity between web search, speech recognition, face recognition, machine translation, autonomous driving, and automatic scheduling. Here you will learn the foundational principles of AI and implement some the AI systems. The goal of this course is to help you tackle the real-world situations with the help of AI tools. So, it is the best for the beginner to get started with AI.
3. Learn with GOOGLE AI
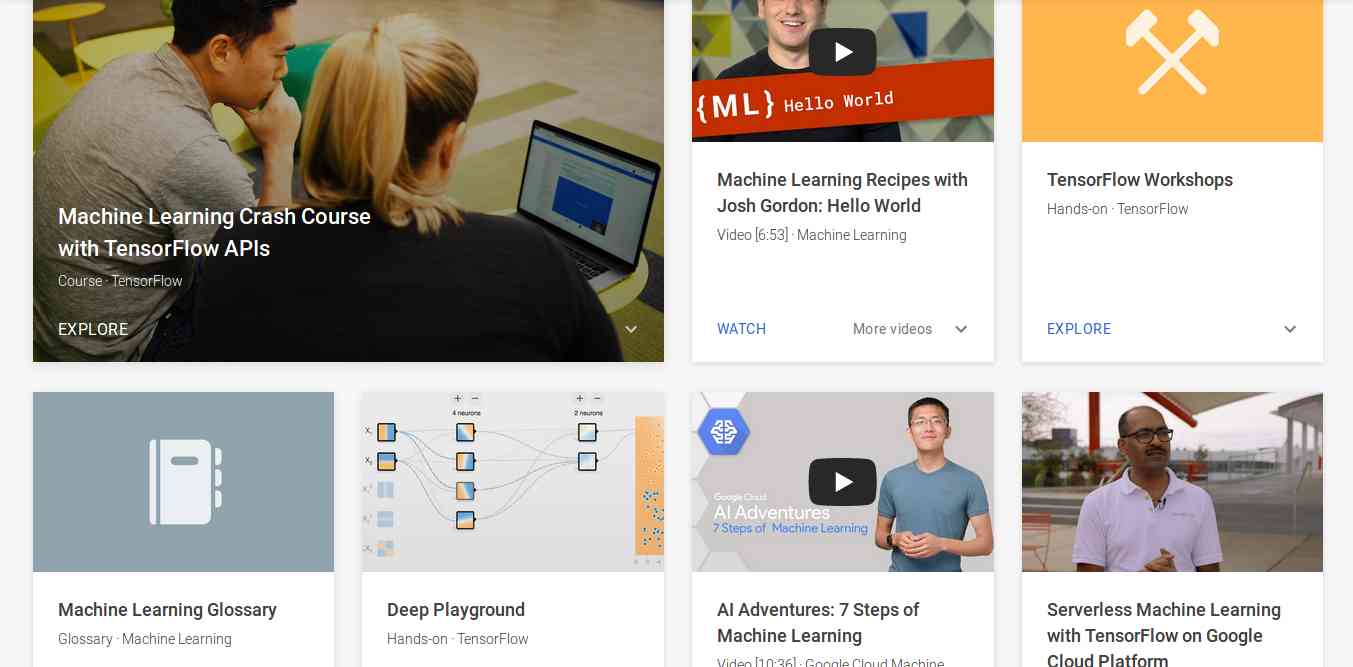
Who will dislike the course from Google? absolutely no one. This company is one of the early adopters of AI has a lot to offer to learners. Learn with Google AI is an education platform for people at all experience levels, it is free to access and browse content. The education resources provided by Google is from the machine learning experts of the company. These resources are the collections of lessons, tutorials, and Hands-on exercises that help you start learning, building, and problem-solving.
4. MIT 6.S094: Deep Learning for Self-Driving Cars
This course gives the practical overview of Deep Learning and AI. It is the course for beginners, also for the people who are getting started with Machine Learning. The course also offers a lot of benefits to the experienced and advanced researchers in the field deep learning. This MIT's course takes people into the journey of Deep Learning with the applied theme of building Self-Driving cars. However, the course also offers slides and videos to engage the learners.
5. Fundamentals of Deep Learning for Computer Vision
This course is offered by Nvidia and Nvidia Deep learning Institute. Computer Vision is one of the disciplines of AI that acquire, analyze, process, and understand images. The course is completely free and everyone who is enthusiast about AI can access and learn the course. It is a hands-on course that able to provide basics of deep learning and deployment of neural networks. With this. you will also learn the following:
- Identify the ingredients required to start a Deep Learning project.
- Train a deep neural network to correctly classify images it has never seen before.
- Deploy deep neural networks into applications.
- Identify techniques for improving the performance of deep learning applications.
- Assess the types of problems that are candidates for deep learning.
- Modify neural networks to change their behavior.
- Ethical Hacking
- Libros Hacking
- Curso De Growth Hacking
- Hacking Marketing
- Blackhat Hacking
- Ethical Hacking Curso
- Growth Hacking Pdf
- Black Hacker
- Blog Seguridad Informática
- Significado De Hacker
- Hacking Wifi Windows
- Ethical Hacking Course
- Growth Hacking Examples
- Que Hay Que Estudiar Para Ser Hacker
- Hacking The System
- Hacking Gif
Sslmerge - Tool To Help You Build A Valid SSL Certificate Chain From The Root Certificate To The End-User Certificate

Is an open source tool to help you build a valid SSL certificate chain from the root certificate to the end-user certificate. Also can help you fix the incomplete certificate chain and download all missing CA certificates.
How To Use
It's simple:
# Clone this repository
git clone https://github.com/trimstray/sslmerge

# Go into the repository
cd sslmerge

# Install
./setup.sh install

# Run the app
sslmerge -i /data/certs -o /data/certs/chain.crt
- symlink to
bin/sslmergeis placed in/usr/local/bin- man page is placed in
/usr/local/man/man8
Parameters
Provides the following options:
  Usage:
    sslmerge <option|long-option>

  Examples:
    sslmerge --in Root.crt --in Intermediate1.crt --in Server.crt --out bundle_chain_certs.crt
    sslmerge --in /tmp/certs --out bundle_chain_certs.crt --with-root
    sslmerge -i Server.crt -o bundle_chain_certs.crt

  Options:
        --help        show this message
        --debug       displays information on the screen (debug mode)
    -i, --in          add certificates to merge (certificate file, multiple files or directory with ssl certificates)
    -o, --out         saves the result (chain) to file
        --with-root   add root certificate to the certificate chain
How it works
Let's start with ssllabs certificate chain. They are delivered together with the sslmerge and can be found in the
example/ssllabs.com directory which additionally contains the all directory (containing all the certificates needed to assemble the chain) and the server_certificate directory (containing only the server certificate).The correct chain for the ssllabs.com domain (the result of the openssl command):
Certificate chain
 0 s:/C=US/ST=California/L=Redwood City/O=Qualys, Inc./CN=ssllabs.com
   i:/C=US/O=Entrust, Inc./OU=See www.entrust.net/legal-terms/OU=(c) 2012 Entrust, Inc. - for authorized use only/CN=Entrust Certification Authority - L1K
 1 s:/C=US/O=Entrust, Inc./OU=See www.entrust.net/legal-terms/OU=(c) 2012 Entrust, Inc. - for authorized use only/CN=Entrust Certification Authority - L1K
   i:/C=US/O=Entrust, Inc./OU=See www.entrust.net/legal-terms/OU=(c) 2009 Entrust, Inc. - for authorized use only/CN=Entrust Root Certification Authority - G2
 2 s:/C=US/O=Entrust, Inc./OU=See www.entrust.net/legal-terms/OU=(c) 2009 Entrust, Inc. - for authorized use only/CN=Entrust Root Certification Authority - G2
i:/C=US/O=Entrust, Inc./OU=www.entrust.net/CPS is incorporated by reference/OU=(c) 2006 Entrust, Inc./CN=Entrust Root Certification Authority- Identity Certificate (Server Certificate)
issued for ssllabs.com by Entrust Certification Authority - L1K
- Intermediate Certificate
issued for Entrust Certification Authority - L1K by Entrust Root Certification Authority - G2
- Intermediate Certificate
issued for Entrust Root Certification Authority - G2 by Entrust Root Certification Authority
- Root Certificate (Self-Signed Certificate)
issued for Entrust Root Certification Authority by Entrust Root Certification Authority
Scenario 1
In this scenario, we will chain all delivered certificates. Example of running the tool:

In this scenario, we only use the server certificate and use it to retrieve the remaining required certificates. Then, as above, we will combine all the provided certificates. Example of running the tool:

In order to create a valid chain, you must provide the tool with all the necessary certificates. It will be:
- Server Certificate
- Intermediate CAs and Root CAs
However, if you look inside the generated chain after generating with sslmerge, you will not find the root certificate there. Why?
Because self-signed root certificates need not/should not be included in web server configuration. They serve no purpose (clients will always ignore them) and they incur a slight performance (latency) penalty because they increase the size of the SSL handshake.
If you want to add a root certificate to the certificate chain, call the utility with the
--with-root parameter.Certification Paths
Sslmerge allows use of two certification paths:

When generating the chain of certificates, sslmerge displays comments with information about certificates, including any errors.
Here is a list of all possibilities:
not found identity (end-user, server) certificate
The message is displayed in the absence of a server certificate that is the beginning of the chain. This is a unique case because in this situation the sslmerge ends its operation displaying only this information. The server certificate is the only certificate required to correctly create a chain. Without this certificate, the correct chain will not be created.
found correct identity (end-user, server) certificate
The reverse situation here - message displayed when a valid server certificate is found.
not found first intermediate certificate
This message appears when the first of the two intermediate certificates is not found. This information does not explicitly specify the absence of a second intermediate certificate and on the other hand it allows to determine whether the intermediate certificate to which the server certificate was signed exists. Additionally, it can be displayed if the second intermediate certificate has been delivered.
not found second intermediate certificate
Similar to the above, however, it concerns the second intermediate certificate. However, it is possible to create the chain correctly using the second certification path, e.g. using the first intermediate certificate and replacing the second with the main certificate.
one or more intermediate certificate not found
This message means that one or all of the required intermediate certificates are missing and displayed in the absence of the root certificate.
found 'n' correct intermediate certificate(s)
This message indicates the number of valid intermediate certificates.
not found correct root certificate
The lack of the root certificate is treated as a warning. Of course, when configuring certificates on the server side, it is not recommended to attach a root certificate, but if you create it with the sslmerge, it treats the chain as incomplete displaying information about the incorrect creation of the chain.
an empty CN field was found in one of the certificates
This message does not inform about the error and about the lack of the CN field what can happen with some certificates (look at
example/google.com). Common Name field identifies the host name associated with the certificate. There is no requirement in RFC3280 for an Issuer DN to have a CN. Most CAs do include a CN in the Issuer DN, but some don't, such as this Equifax CA.Requirements
Sslmerge uses external utilities to be installed before running:
Other
Contributing
See this.
Project architecture
See this.
More articles
Subscribe to:
Posts (Atom)


